Exchange Risk Controls That Stop Illicit Flows
A suspicious withdrawal is rarely an isolated event. It may be the final movement in a chain that began with a phishing theft, pig-butchering fraud, ransomware payment, sanctions evasion attempt, or money laundering operation. Effective exchange risk controls give compliance and investigations teams the ability to see that chain, assess its significance, preserve the record, and intervene before assets move beyond reach.
For centralized exchanges, payment providers, and financial institutions serving digital asset customers, the central challenge is not simply identifying high-risk wallets. It is making defensible decisions at operational speed. A useful control environment must connect blockchain intelligence to customer activity, case management, escalation procedures, and lawful action.
What Exchange Risk Controls Must Accomplish
Exchange controls should reduce exposure without treating every unusual transaction as criminal. High transaction volume, rapid asset swaps, or use of self-custody wallets can be legitimate. Context determines whether activity creates a money laundering, sanctions, fraud, or public-safety concern.
That context comes from combining on-chain and off-chain evidence. On-chain intelligence can reveal direct and indirect exposure to ransomware infrastructure, sanctioned entities, darknet markets, fraud clusters, mixers, bridge exploits, or high-risk services. Exchange records can establish the customer relationship, account behavior, fiat rails, device information, withdrawal patterns, and prior alerts. Neither source is sufficient on its own.
A control framework should support four operational outcomes: identify risk early, prioritize the cases that require action, preserve evidence in a reviewable form, and execute a proportionate response. The response may range from enhanced due diligence to transaction delay, account restriction, suspicious activity reporting, law enforcement notification, or a targeted freeze request where lawful authority and evidence support it.
Core Exchange Risk Controls Across the Customer Lifecycle
Risk-based onboarding and customer profiling
Controls begin before the first deposit. Customer due diligence should establish who is opening the account, the expected purpose of the relationship, relevant geography, source-of-funds indicators, and exposure to elevated-risk sectors or jurisdictions. For institutional accounts, beneficial ownership and expected transaction activity require particular scrutiny.
Static screening alone has limits. A customer may pass sanctions and identity checks at onboarding yet later receive assets connected to a newly identified fraud scheme or sanctioned service. Exchanges need periodic review and event-driven reassessment when behavior departs materially from the customer profile.
Deposit and withdrawal screening
Wallet screening is most effective when it is integrated into transaction decisioning rather than treated as a retrospective reporting exercise. Incoming deposits should be assessed for exposure to known illicit entities, while outgoing withdrawals should be evaluated for destination risk and behavior that indicates asset dissipation.
Risk scoring should account for more than direct exposure. Criminal proceeds often move through multiple hops, swaps, bridges, and intermediary wallets before reaching an exchange. A model that only flags direct contacts will miss meaningful indirect connections. At the same time, overly broad exposure rules can create high volumes of low-value alerts. Teams need adjustable thresholds based on asset type, typology, customer risk, transaction value, timing, and the quality of attribution.
Behavioral monitoring and typology detection
The most valuable alerts often emerge from combinations of signals. A newly opened account that receives fragmented deposits from wallets tied to a fraud network, converts funds quickly, and withdraws to fresh addresses presents a different risk profile than a long-standing customer moving assets to a known personal wallet.
Monitoring scenarios should reflect the threats facing the institution. Relevant patterns may include rapid peel chains, structuring across accounts, cross-chain layering, conversion after exploit proceeds arrive, deposits following mixer activity, mule-account behavior, and coordinated withdrawals linked by shared infrastructure. Controls should also account for scam typologies that use legitimate exchanges as cash-out points, including investment fraud, business email compromise, romance scams, and account takeover.
Sanctions controls that follow the funds
Sanctions risk is not confined to a published wallet address list. Designated actors change infrastructure, use intermediaries, and rely on nested services or cross-chain transfers to obscure source and destination. Exchanges need continuous intelligence updates and tracing capabilities that identify meaningful links to sanctioned networks, even when the observed address is not itself designated.
This does not mean every indirect connection warrants automatic rejection. The strength of the connection, time elapsed, transaction path, amount, and corroborating account evidence all matter. The key is a documented decision process that explains why the institution escalated, restricted, cleared, or reported the activity.
From Alert Volume to Investigative Action
An alert queue is not a control. It becomes a control only when trained personnel can validate the signal, document findings, and trigger timely action.
First-line review should resolve straightforward false positives and gather the account facts necessary for escalation. Higher-risk cases require investigators who can trace funds across chains, interpret entity attribution, assess clustering evidence, and distinguish a direct criminal nexus from weak proximity. For cases involving victim losses or active threats, speed matters because assets can be exchanged, bridged, or withdrawn within minutes.
Case management is essential. Each investigative file should retain the alert rationale, transaction identifiers, wallet addresses, attribution sources, tracing path, customer information, analyst notes, decisions, approvals, and communications with external counterparts. This record supports internal governance and helps establish a clear evidentiary trail for regulators, law enforcement, counsel, and potential recovery action.
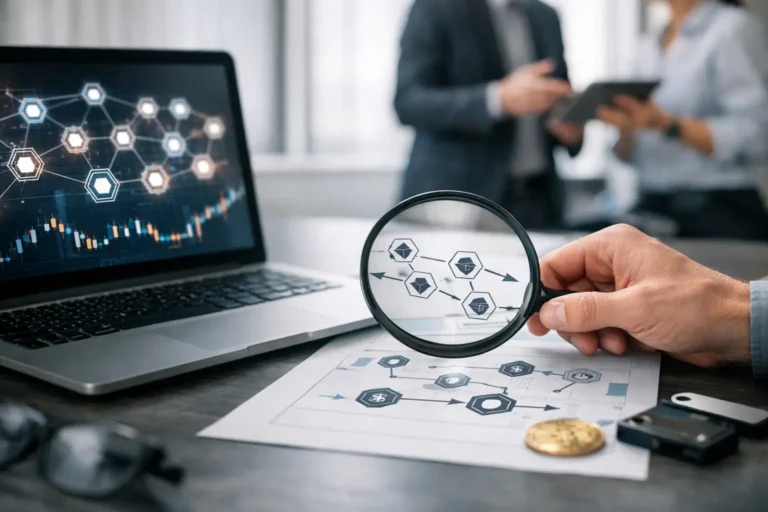
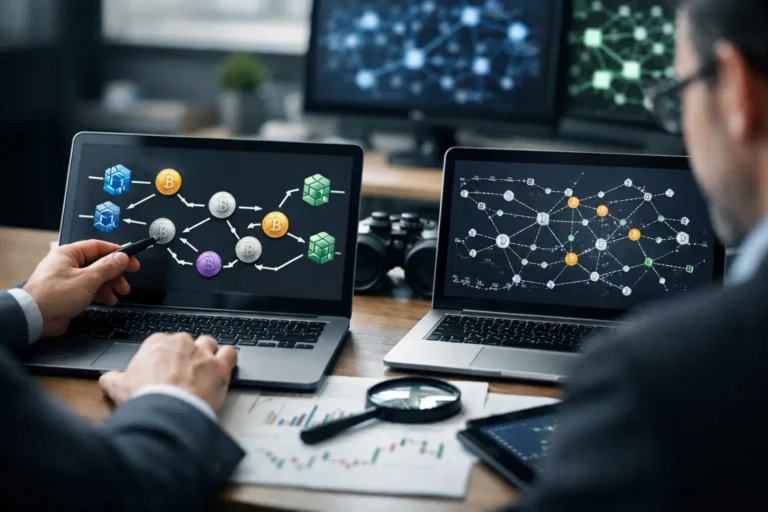
Visual transaction analysis can materially improve decision quality in complex cases. A graph that shows the movement from a compromised wallet through intermediary addresses to an exchange account can expose patterns that a spreadsheet obscures. Visualization is especially useful when investigators must explain an asset flow to non-technical stakeholders or support a request for urgent intervention.
Designing Controls for Fast, Defensible Intervention
High-risk cases need predefined escalation paths. Waiting for multiple manual approvals after an investigator identifies ransomware proceeds or a major fraud cash-out can eliminate the opportunity to contain the funds. Conversely, unrestricted authority to freeze accounts can create legal, customer, and operational risk. The answer is a clear decision matrix with designated authorities, evidence standards, and time-bound review requirements.
An effective matrix distinguishes between actions. Enhanced due diligence may be appropriate where risk is concerning but evidence is incomplete. A temporary transaction hold may be justified while facts are verified. Account restriction, formal reporting, or cooperation with law enforcement may be necessary when the evidence establishes a stronger nexus to illicit activity. Policies should define when external freeze requests can be accepted and what documentation is required to act on them.
Exchange teams should test these procedures before a crisis. Tabletop exercises can reveal whether fraud operations, compliance, legal, customer support, and security teams know who owns the decision, how evidence is transferred, and how customer communications are handled. The objective is not merely policy compliance. It is preventing a known illicit flow from becoming unrecoverable.
Common Gaps That Undermine Exchange Controls
Many programs fail at the handoff between detection and action. Screening may identify a concerning address, but the alert lacks transaction context. Investigators may trace funds successfully, but evidence is scattered across tools and cannot be quickly shared. Legal teams may receive an urgent request without a documented basis for the proposed restriction.
Other common weaknesses include relying on static attribution, failing to monitor cross-chain activity, treating all mixer exposure as identical, and using alert thresholds that do not reflect the exchange’s customer base or threat profile. A control that produces too few alerts can miss criminal activity. One that produces too many can bury investigators in noise and delay the cases that matter most.
Control effectiveness should therefore be measured beyond alert counts. Leadership should examine time to triage, time to escalation, false-positive rates, quality of case documentation, repeat exposure by customer segment, and the outcome of interventions. Where permitted, teams should also track funds preserved, freezes supported, referrals accepted, and victim-loss disruption outcomes.
Building an Intelligence-Led Operating Model
The strongest exchange programs treat blockchain intelligence as an operational layer, not a standalone vendor feed. Intelligence must reach the people making transaction decisions, investigators building cases, and external partners capable of disrupting illicit movement.
That requires coverage across relevant blockchains, including assets and networks criminals use for speed, liquidity, and obfuscation. It also requires de-mixing analysis, entity intelligence, and investigators who understand how to state analytical conclusions with appropriate confidence. Aegis Financial Forensics supports this model by connecting tracing, visual investigation, evidentiary analysis, and disruption-oriented case workflows.
The practical test is simple: when suspicious assets reach your platform, can your team explain where they came from, what they are connected to, who may be affected, and what lawful action can still protect the funds? Exchange risk controls are effective when that answer arrives before the next withdrawal is confirmed.